VPN
A tunnel that is
fully managed
Anyone who accesses company applications from a home office, on the road or from a second site needs a route that is encrypted and controlled. We set up the gateways, manage the access and run the connections.
Encrypted access
Managed VPN
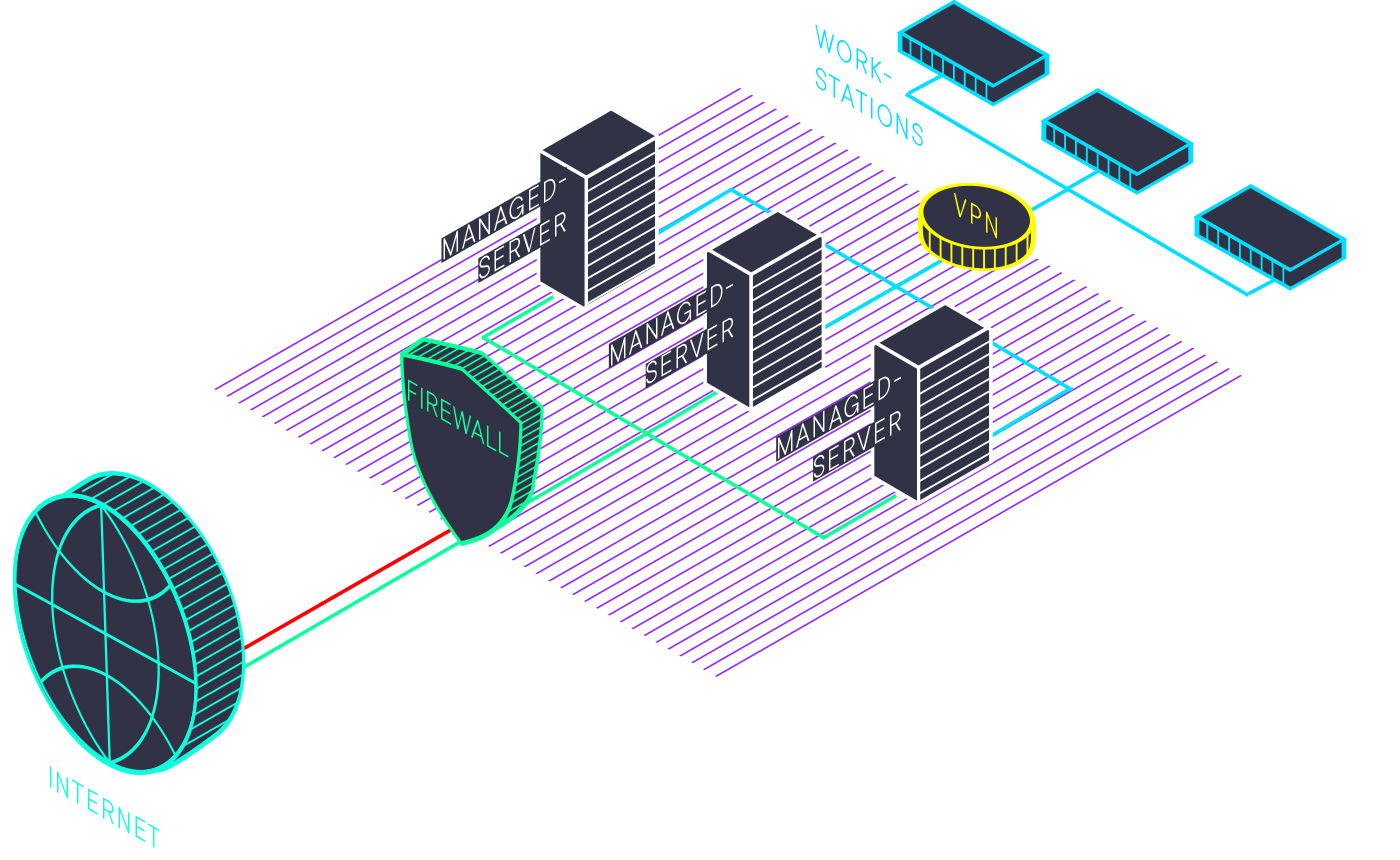
Protect access to your systems in our data centre with our VPN gateways based on IPsec and OpenVPN. With these gateways, we provide secured administrative access to the company applications run in the data centre.
We also make it possible to run remote workplaces securely for your staff, over VPN connections that we manage completely. That way, applications at different sites can be connected to one another and reached in encrypted form.
For access to the VPN, we offer several security mechanisms, including the use of security certificates as well as additional functions such as multi-factor authentication (MFA) and integration with LDAP or Active Directory for central user management.
Use cases
What a managed VPN is needed for
Remote access
Staff reach company applications from home or on the road over an encrypted connection.
Linking sites
Two or more sites are connected through fixed tunnels, so that applications stay reachable across sites.
Administrative access
Administration does not run over the open internet but over a controlled route that can be logged.
Central user management
Access is tied to LDAP or Active Directory. Whoever leaves the company loses access in one place.
Technology
What the VPN is built on
We run the gateways based on IPsec and OpenVPN. Which protocol fits depends on the remote ends: IPsec is widespread in networking and links sites reliably; OpenVPN is more flexible for individual access across different operating systems.
Authentication runs over security certificates, with multi-factor authentication in addition on request. We connect user management to your existing directory instead of maintaining a second user database.
- IPsec and OpenVPN
- Security certificates
- Multi-factor authentication (MFA)
- LDAP or Active Directory integration
- Site-to-site and individual access
- Operation and upkeep by kyberio
Frequently asked questions about the managed VPN
What does "managed" mean for the VPN?
We set up the gateways, configure the tunnels, manage certificates and access, keep the updates in order and run the connections. You do not have to keep track of gateway software or certificate lifetimes.
IPsec or OpenVPN?
Both are possible. IPsec is widespread in networking and well suited to linking sites permanently. OpenVPN is more flexible for individual access across different operating systems. Which variant fits depends on your remote ends and devices.
Is there multi-factor authentication?
Yes. In addition to security certificates, multi-factor authentication can be set up. We also connect LDAP or Active Directory, so that access is granted and withdrawn centrally.
Can I use it to connect several sites?
Yes. With site-to-site connections, applications at different sites can be connected to one another and reached in encrypted form.
What systems do the gateways run on?
That depends on the setup. For manageable setups, the VPN is a function of the managed firewall — rules and tunnels are then in the same place, which keeps things clear. Where many tunnels or a lot of throughput come together, we put separate gateways in front, so that firewall and VPN do not slow each other down. What fits in your case we work out beforehand.
Do you offer zero trust network access?
Not as a product. What we run is classic VPN using IPsec and OpenVPN — with multi-factor authentication, certificates and centrally granted access. Individual principles from zero trust thinking can be implemented with it, such as sign-in through Keycloak and separate access for each application. But it is not a ZTNA product that checks every connection individually — and we do not call it one.
What response times do you commit to?
We monitor around the clock, every day of the year. How quickly we intervene and through which escalation stages is set out in your contract — a time we have not committed to is not a time we state here.
Satisfied customers

Sovereignty
Paving the way for digital sovereignty
-
Owner-managed since 1997
As an owner-managed operator with our own data centers, we make our decisions independently and are subject exclusively to German / EU law.
-
100% made in Germany
Our data center, product development, and customer support are all based in Germany for your digital sovereignty.
-
24/7 Customer Support
We are here for you: 24/7/365 customer support, in English and German
Let us find the right solution together
We take the time to understand what you need and to develop solutions that fit. We explain complicated technical matters clearly and precisely as we go. Get in touch with me directly and we will work it out.

- We will get back to you as soon as we can.
- No obligation, free of charge.